Connect an AI coding tool (MCP)
AOZUMI is an MCP server. Give a coding tool such as Claude Code, Cursor or Codex a key and it can take a repository from inspection to a share link, pausing wherever a person needs to decide. For the bigger picture, see how agents work with AOZUMI.
Create an agent key
- Open your ProfileSign in and open the avatar menu, then Profile, or go straight to Deploy from Cursor or Claude. Finish workspace setup first if you have not.
- Create a named keyUnder Your agent keys, name it after the client, such as “Claude Code laptop”, choose its Access and Expires, and select Create agent key.
- Copy it nowAOZUMI shows a new key once and stores only a hash of it. Keys start with
slt_.
A key acts as you, in its workspace, limited to the access level you choose (Read, Deploy or Manage) and an optional expiry; see access levels. Agents that should create share links or pause and resume apps need Manage, as do agents that create AOZUMI DB databases, show their tokens or write to them; Deploy covers check, import, secrets, deploy, status and logs, and the operating tools apps, deployments, variables, rollback and cancel. Read also lists databases and runs read-only SQL. Select Revoke beside a key at any time; the next request with it is refused.
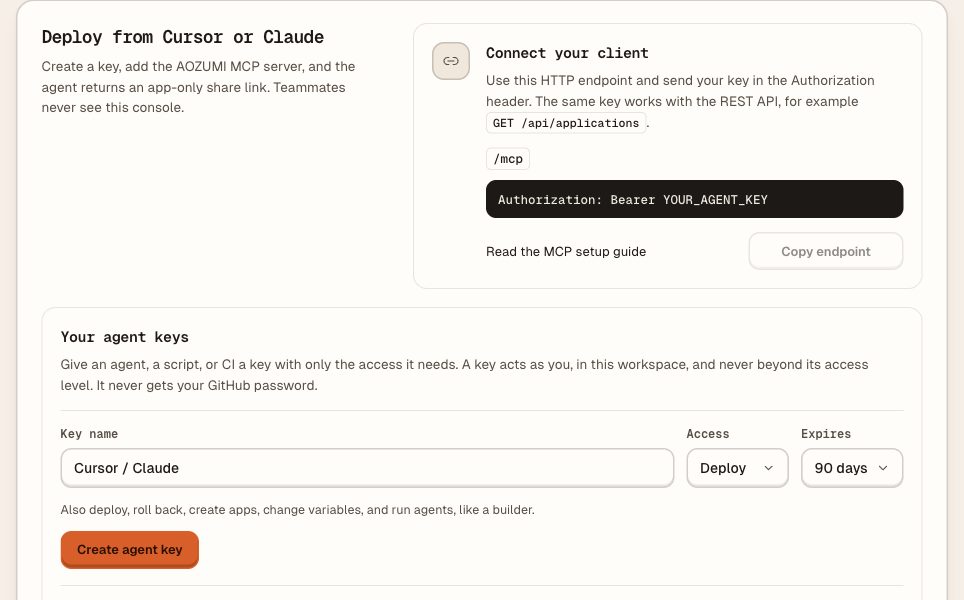
Connect a client
- Endpoint
https://aozumi.dev/mcp- Transport
- HTTP, JSON-RPC 2.0. Protocol version
2025-06-18; clients on2025-03-26or2024-11-05still connect. - Authentication
X-API-Key: <agent key>, orAuthorization: Bearer <agent key>
Claude Code
claude mcp add --transport http aozumi https://aozumi.dev/mcp \
  --header "X-API-Key: $AOZUMI_AGENT_KEY"
Clients that use a JSON config
For a project .mcp.json in Claude Code, and similar mcpServers files in other clients. ${AOZUMI_AGENT_KEY} reads the key from your environment; check how your client expands variables.
{
  "mcpServers": {
    "aozumi": {
      "type": "http",
      "url": "https://aozumi.dev/mcp",
      "headers": {
        "X-API-Key": "${AOZUMI_AGENT_KEY}"
      }
    }
  }
}
Clients that only start a local command
These cannot connect yet. Use a client that supports remote HTTP MCP servers with custom headers.
Tools
Listing tools needs no key. Calling one does.
| Tool | Arguments | What it does |
|---|---|---|
check | repository | Inspect a GitHub repository for deploy blockers, secrets, data needs, and unsafe capabilities. Returns an inspectionReceipt for import. Does not deploy. |
import | inspectionReceipt, safetyAccepted?, audience? | Create or update a AOZUMI application from an inspectionReceipt. Requires safetyAccepted=true when the review status is review. |
secrets | applicationId, secrets[{ key, value }] | Store encrypted environment variables for an application. Call after check/import when missingVariables are listed. |
deploy | applicationId | Queue a production deploy. Returns immediately; poll status until live. |
status | applicationId | Latest deploy state, runtime lane (fast wake on Lambda or always on), protected gateway URL, missing setup, and any existing share link. |
logs | applicationId, environmentId?, tail? | Read the latest deployment logs for one environment. Returns redacted, size-bounded output and AOZUMI's diagnosis; defaults to Production. |
traffic | applicationId, environmentId?, deploymentId?, range? (1h, 24h, 7d or 30d) | Read visitor traffic for one environment from AOZUMI analytics: requests, server error rate, p50/p95/p99 latency, top paths, countries, a per-release comparison and a regression hint when the newest release is clearly worse. Defaults to Production and the last 24 hours. |
firewall | applicationId, rules? (replaces all), settings? (omit both to read) | Read an app's firewall (settings, rules, recent decisions), or save it when rules or settings is passed. Rules match ip (CIDR), country, path (prefix or glob), method and user_agent (contains), then allow, deny, challenge or log, by ascending priority. settings: enabled, logOnly (record without blocking), rateLimit { requests, period: 10|60 } per client IP. Passing rules replaces all of them. |
share | applicationId, duration? | Mint a week-long app-only share URL when the owner asks for one. It replaces (revokes) any existing link for the environment. Teammates open the app, not GitHub or the AOZUMI console. Requires a live protected deploy. |
apps | none | List applications in the agent key's workspace with lifecycle and latest deploy state. Use to find an applicationId. |
deployments | applicationId, environmentId?, limit? | Recent deployments for an application, newest first, with status and source commit. Use a live deployment id with rollback. |
variables | applicationId | Names of stored environment variables for an application. Values are never returned. |
rollback | applicationId, deploymentId, environmentId? | Restore a previous healthy deployment in the same environment. Get deploymentId from deployments. |
cancel | applicationId, environmentId? | Cancel the queued or building deployment. The current live release keeps serving. |
lifecycle | applicationId, action (pause or resume), environmentId? | Pause an application (stops serving) or resume a paused one. Requires workspace owner or admin. |
log_drains | applicationId, action (list, add, test, pause, resume or remove), drainId?, name?, url?, format?, sources?, samplingPercent?, header? | List, add, test, pause, resume or remove HTTPS log drains for an app (build logs, runtime logs, deploy events; NDJSON or JSON, HMAC-signed). add returns the signing secret once. Adding or changing a drain needs a manage-scoped key. |
databases | none | List the AOZUMI DB databases in the agent key's workspace (SQLite-compatible, reached with @libsql/client): name, id, status, size, and the app environment each serves. Also says whether the workspace may create databases and whether this key may manage them. Use a name or id with the other database tools. |
database_create | name | Create a standalone AOZUMI DB database. The name is lowercase letters, digits and hyphens, at most 40, unique in the workspace; a workspace has at most 3 databases. Needs a Manage key. Then call database_token for its URL and token. |
database_token | database, access? (read-write or read-only) | Show a standalone database's URL and token, with env: the two .env lines (AOZUMI_DB_URL, AOZUMI_DB_TOKEN) to connect with @libsql/client. access is read-write (the default) or read-only. The token has no expiry and is the same on every call until database_rotate_token; each call is in the workspace's audit log, naming this key. Needs a Manage key. Keep tokens out of commits and chat. |
database_rotate_token | database | Revoke every token shown for a standalone database, read-only ones too; the next database_token returns a new one. If the database is handed to an app environment, that app loses it until it is redeployed with the new AOZUMI_DB_TOKEN, which AOZUMI sets. Needs a Manage key. |
database_sql | database, sql, write?, confirm? | Run SQL on a database. Statements run in order, the first error stops the rest, an open transaction is rolled back, and up to 1,000 rows per statement come back. Read-only unless write is true, which needs a Manage key. With write, a script that destroys data (DROP, or DELETE or UPDATE without WHERE) fails with error.code confirm_destructive and lists the statements: show them to the person and send again with confirm true only if they agree. For app traffic, connect with database_token instead. |
database_schema | database | A database's tables and their columns (name, type, not null, primary key). |
database_backups | database | A database's backups, newest first (id, takenAt, sizeBytes, kind: scheduled, manual or before_restore), the moments it can be restored to (window.earliest to window.latest, ISO times), how its backups are going (status.lastBackupAt, status.upToDateAt, status.failingSince) and how many days its workspace's plan keeps them (retentionDays). Any key that can read the database. |
database_backup | database | Back up a database now, for example before a migration or a risky change; restore from it with database_restore. At most one a minute per database: sooner fails with error.code too_soon and retryAfterSeconds. Needs a Manage key. |
database_restore | database, into (new or in_place), backup? or at?, name? (new), confirm? (in_place: the name again) | Restore a database from a backup (backup: its id from database_backups, or latest) or a moment (at: an ISO time inside the window). into new makes a standalone database named name from it, under the workspace's cap of 3; the original stays. into in_place replaces the database's data and keeps its URL, tokens and the app it serves; AOZUMI keeps what it replaced as a before_restore backup, and restoring that undoes it. In place needs confirm: the database's name typed again. Ask the person first. Needs a Manage key. |
database_delete | database, confirm (the name again) | Delete a database and all its data; this cannot be undone. Pass confirm: the database's name again (a standalone database's name, or an app database's databaseName from databases). Needs a Manage key. Ask the person first. |
import takes an audience of “My team” (the default, shown as Workspace in the console), “Only me” or “Specific people” (both shown as Invited people only). share takes a duration of day, week (the default) or month, and returns the active link if there already is one.
The usual flow
- checkInspect the repository. Show the findings and required variables to the person.
- importPass the
inspectionReceiptfrom check. Stop if the review is blocked. - secretsOnly if import listed
missingVariables. - deployQueues a Production deploy and returns at once.
- statusPoll until the app is healthy. If the deploy failed, call
logs. - shareCreate an app-only link once the deploy is live and protected.
To operate an app that already exists, call apps to find it, deployments, logs and traffic (requests, error rate and latency per release) to see what happened, and then rollback, cancel, lifecycle or deploy again. Each tool says whether it is read-only or destructive, so a client can ask before it changes anything. Failed calls return a machine-readable error.code such as not_found or forbidden.
For a database: databases, then database_create, database_token for the two .env lines, and database_sql. Before a risky change, database_backup; to go back, database_restore. See AOZUMI DB from a coding agent.
Every tool result includes a next field that tells the agent what to do next, so clients do not need to hard-code this order. A good first prompt:
Check my repository with AOZUMI. Explain any blockers, required variables and review findings, and wait for my approval before importing, deploying or creating a share link.
Safety model
- Review gate. A blocked review cannot be imported. A review with findings needs
safetyAccepted: true; AOZUMI records the decision with the commit and the person. - Signed receipts. The inspection receipt is signed, tied to your user and workspace, and expires after 15 minutes, so an agent cannot import something that was never checked.
- Write-only secrets. The
secretstool returns the names it stored, andvariableslists names only, never values. - Database tokens on request. Only Manage keys get a token from
database_token, and each reveal is in the audit log with the key's prefix.database_sqlruns read-only unlesswriteis set, and a script that destroys data waits forconfirm. Keys made before access levels cannot use the database tools. - Separate keys. Agent keys and CLI keys are different. A key from
aozumi loginor Hachi's sign-in is refused here. - Revocation. Revoke a key on your Profile, under Your agent keys, and it stops working on the next request.
Call it directly
MCP is JSON-RPC over HTTP, so curl works for testing. List the tools:
curl -s https://aozumi.dev/mcp \
  -H "content-type: application/json" \
  -d '{"jsonrpc":"2.0","id":1,"method":"tools/list"}'
Call check with your key:
export AOZUMI_AGENT_KEY="slt_your_agent_key"

curl -s https://aozumi.dev/mcp \
  -H "content-type: application/json" \
  -H "X-API-Key: $AOZUMI_AGENT_KEY" \
  -d '{
    "jsonrpc": "2.0",
    "id": 2,
    "method": "tools/call",
    "params": {
      "name": "check",
      "arguments": { "repository": "your-org/your-repo" }
    }
  }'
Troubleshooting
401 and “Create an agent key at /profile”
The key is missing, revoked, mistyped or a CLI key. Send an active agent key in X-API-Key.
Tools list, but calls fail
Listing tools needs no key; calls need a valid key, workspace access, and for private repositories, the AOZUMI GitHub App installed on that repository.
The client asks for browser OAuth
This endpoint uses API-key headers. Choose a client setting that supports custom headers.
Import is refused
Read the error. A blocked review needs a change in the repository; a review with findings needs a person to accept them; an expired receipt needs a fresh check. Retrying alone does not help.
Questions
- Can an AI coding tool deploy to AOZUMI?
- Yes. Connect an MCP client to https://aozumi.dev/mcp with an agent key from your Profile, under Deploy from Cursor or Claude, sent as the X-API-Key header. The agent can check a repository, import it, set secrets, deploy, poll status, read logs and create a share link, then operate the app: list apps and deployments, roll back, cancel a deploy, or pause and resume it. It can also manage AOZUMI DB databases.
- Can an agent bypass AOZUMI's security review?
- No. Import refuses a repository whose review is blocked. When the review needs a decision, import fails unless safetyAccepted is true, which an agent should send only after showing you the findings. AOZUMI records who accepted them and for which commit.
- What is the difference between an agent key and a CLI key?
- Agent keys are created on your Profile, under Deploy from Cursor or Claude, for MCP clients and the REST API. CLI keys are created by aozumi login, and Hachi signs in the same way; those keys deploy from the CLI in the approved workspace and run AOZUMI Agents, and the MCP endpoint refuses them.
- Can MCP manage AOZUMI Agents?
- No. The MCP tools cover apps and AOZUMI DB databases. AOZUMI Agents, the cloud agents you talk to in Hachi, is a separate product, documented under Agents; a Manage key reaches them only through the REST API.
- Does the MCP endpoint support OAuth?
- No. It uses an API key in a request header. Use a client that supports remote HTTP MCP servers with custom headers.
Checked against the product on .